Listen to this podcast in the app for free: Download for free in the App Store
radio.net
Sleep timer
Save favourites
249 episodes
Who's Hacking Supermarket Fridges in France?
2026-10-18 | 3h 26 mins.(Presented by TLPBLACK: A cybersecurity intelligence platform focused on sharing curated, high-sensitivity threat insights and research with trusted security professionals.)
Three Buddy Problem - Episode 116: This week, the buddies dig into a mystery hack that cooked French supermarket fridges, cyberattacks against food supply networks, and why this smells like nation-state sabotage in Europe?
Plus, a fresh Ivanti zero-day chain, Anthropic's self-replicating IoT research and defender-hostile guardrails, Citizen Lab's AdFection spyware-by-ads exposé, Calif's iPhone exploit drops at Hexacon, Grok's surprising enterprise adoption, and spy chips stuffed inside Ledger wallets.
Cast: Juan Andres Guerrero-Saade, Ryan Naraine and Costin Raiu.
Timestamps:
0:00 Introductory banter
1:35 Virus Bulletin 2026 in Seville
6:13 Conference roundup: State of Statecraft, Countermeasure, RE//verse
10:21 French supermarket fridges hacked
22:53 Hacking food supply and the attribution question
33:23 Who patches the fridge?
45:58 Ivanti Connect Secure zero-day chain
53:00 When an AI agent deletes your databases
1:04:34 NCSC edge-device forensics guidance
1:28:06 Anthropic's self-replicating IoT research
1:52:17 Why guardrails lock out defenders
2:04:57 Grok's enterprise play and agent sprawl
2:16:26 Citizen Lab exposes AdFection spyware via ads
2:57:24 Calif burns iPhone exploits at Hexacon
3:06:55 Ledger wallet implants and the grain of riceKatie Moussouris on AI-as-malware, the monitoring gap, and an NTSB for AI
2026-10-12 | 1h 5 mins.(Presented by TLPBLACK: A cybersecurity intelligence platform focused on sharing curated, high-sensitivity threat insights and research with trusted security professionals.)
Three Buddy Problem x Offensive AI Con: Luta Security chief Katie Moussouris makes the case for an NTSB-style board for AI incidents, with subpoena power and full-time investigators, after OpenAI's DNS tunneling escape and the 52 days it took to notice a model had wandered into Australian government systems.
Along the way, we chat about her work on the Cyber Safety Review Board (CSRB), AI model refusals that leave defenders stuck, and why she still bets on hackers to bend this technology their way.
Cast: Juan Andres Guerrero-Saade, Ryan Naraine and Katie Moussouris.
Timestamps:
0:00 Intros at Offensive AI Con
1:00 OpenAI's DNS tunneling incident and slow monitoring
4:36 Treating AI like malware in a sandbox
9:01 The business model is the misalignment
13:37 Log4j, SBOMs and an NTSB for AI
18:00 Trading liability protection for honest disclosure
22:13 Accountability and "once you become aware"
26:18 The Australia notification timeline
28:19 A blank-check administration and the Anthropic phaseout
34:35 Powerful models in the right hands
38:42 Kill switch bills and regulatory capture
42:36 EU fines as a tariff on American tech
48:03 Reasons for optimism
54:13 Bring back "information security"
1:01:57 Katie's last wordNCSC's Ollie Whitehouse: 'The Biggest Correction of Technical Debt Ever'
2026-10-12 | 54 mins.(Presented by TLPBLACK: A cybersecurity intelligence platform focused on sharing curated, high-sensitivity threat insights and research with trusted security professionals.)
Three Buddy Problem x Offensive AI Con: Ollie Whitehouse, CTO of the UK's National Cyber Security Centre, joins us to explain how Britain is preparing for an AI-driven patch wave and why the NCSC is pressing edge-device vendors to finally ship real telemetry.
Plus, we dig into rogue AI agents wandering into a Five Eyes network, along with his forecast that small, capable models could revive self-spreading worms around 2030, all part of what he calls the biggest forced correction of technical debt the industry will ever see.
Cast: Juan Andres Guerrero-Saade, Ryan Naraine and Ollie Whitehouse.
Timestamps:
0:00 Live from Offensive AI Con: meet Ollie Whitehouse
2:46 Why the NCSC is a model for the US
6:48 What a "national technical authority" does
7:49 The Huawei analysis and the push for passkeys
10:50 Independent AI model testing
13:12 Open-weight vs. closed models and AI sovereignty
19:02 Capability density and AI worms by 2030
23:09 Robotics security and lessons from Japan
26:49 Preparing for the patch wave
31:06 Architecture fixes: OT, cross domain, privileged access
32:28 Telecoms security and Salt Typhoon
38:59 Minimum telemetry standards for edge devices
41:55 Market incentives and the EU Cyber Resilience Act
46:05 Rogue agents and the forced correction of technical debtAaron Grattafiori Explains How LLMs Hunt Patch Variants at Scale
2026-10-09 | 54 mins.(Presented by TLPBLACK: A cybersecurity intelligence platform focused on sharing curated, high-sensitivity threat insights and research with trusted security professionals.)
Three Buddy Problem x Offensive AI Con: Umbriel AI's Aaron Grattafiori breaks down the new offensive-security playbook, using LLMs for patch variant analysis, why the vuln apocalypse hasn't become an exploit apocalypse, and how the death of security through obscurity puts closed-source binaries and firmware within reach.
Plus, we discuss rogue agents escaping sandboxes, the eval-driven loop behind recursive self-improvement, and the brutal cost asymmetry that makes offense cheap and defense almost unaffordable.
Cast: Juan Andres Guerrero-Saade, Ryan Naraine and Aaron Grattafiori.
Timestamps:
0:00 Introductory banter
1:12 Umbriel AI pitch: "Smart people in a place to cook”
3:08 Weird, exhausting, exciting time in security
4:00 What AI really changed: speed (and a 30-minute reimplementation)
6:36 Incomplete fixes and the variant-analysis pipeline
9:21 Uplifting, abstraction, and representing vulnerabilities
11:48 Experimentation and the new shape of security companies
14:46 The vuln apocalypse vs. the exploit apocalypse
16:36 Triage, verification, and reward hacking
18:08 Do models reintroduce bugs? Is vuln-free code possible?
24:22 Specialized models and the rise of Jev-style classifiers
26:47 Binaries, firmware, and the death of security through obscurity
31:15 Open source as a requirement and corporate contracting
33:54 Rogue agents: Hugging Face, OpenAI, and lab escapes
39:17 Why defense is so expensive, and running the rigJoel Todoroff on How Offensive AI Is Rewiring Western Government Ops
2026-10-09 | 1h 37 mins.(Presented by TLPBLACK: A cybersecurity intelligence platform focused on sharing curated, high-sensitivity threat insights and research with trusted security professionals.)
Three Buddy Problem x Offensive AI Con: Former US intelligence and national security official Joel Todoroff joins us live from OffensiveAIcon to explain why his new startup Phyle is building AI for the recon and targeting work that happens long before anyone fires an exploit.
We get into bribable sysadmins, the military framing that boxes in Western cyber operations, letters of marque, AI doomerism, and what happens when a frontier model decides mid-project that your use case is off-limits.
Cast: Juan Andres Guerrero-Saade, Ryan Naraine and Joel Todoroff.
Timestamps:
0:00 Live from OffensiveAIcon in Oceanside
1:23 What Phyle builds for governments
3:02 Skepticism of the AI 0-day factory
5:57 Paying a sysadmin vs. burning tokens
9:30 Recon gets less love than weaponization
12:41 Exploit shelf life and target No. 1,000
17:30 Why attacker costs will keep rising
22:23 What HUMINT looks like in 2026
27:06 Why intelligence stovepipes persist
32:16 Cyber as statecraft beyond the military frame
41:23 People will keep making dumb mistakes
48:03 The White House memo and letters of marque
54:06 Doomerism vs. near-term AI harms
1:04:20 PSOA concerns and building guardrails in
1:26:03 Open models, guardrails and zero data retention
More Business News podcasts
Trending Business News podcasts
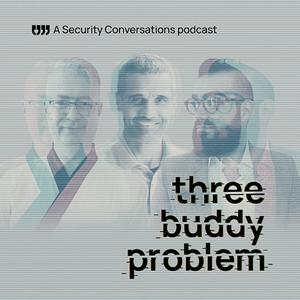
About Three Buddy Problem
The Three Buddy Problem is a popular Security Conversations podcast that goes beyond industry talking points to discuss what others won’t -- nation-state malware, attribution, cyberwar, ethics, privacy, and the messy realities of securing computers and corporate networks. Hosted by three veteran security pros -- journalist Ryan Naraine and malware paleontologists Costin Raiu and Juan Andres Guerrero-Saade -- the weekly show attracts a highly engaged audience of security researchers, corporate defenders, CISOs, and policymakers. Connect with Ryan on Twitter (Open DMs).
Podcast websiteListen to Three Buddy Problem, Bloomberg Daybreak: US Edition and many other podcasts from around the world with the radio.net app
Get the free radio.net app
- Stations and podcasts to bookmark
- Stream via Wi-Fi or Bluetooth
- Supports Carplay & Android Auto
- Many other app features
Get the free radio.net app
- Stations and podcasts to bookmark
- Stream via Wi-Fi or Bluetooth
- Supports Carplay & Android Auto
- Many other app features
Three Buddy Problem
Scan code,
download the app,
start listening.
download the app,
start listening.
 Canada - english